
Public Sector TLS Trends
Ongoing research into how federal and public-sector domains handle TLS, certificate hygiene, and Web PKI shifts.
5 posts · latest June 9, 2026
 Part 1·May 11, 2026
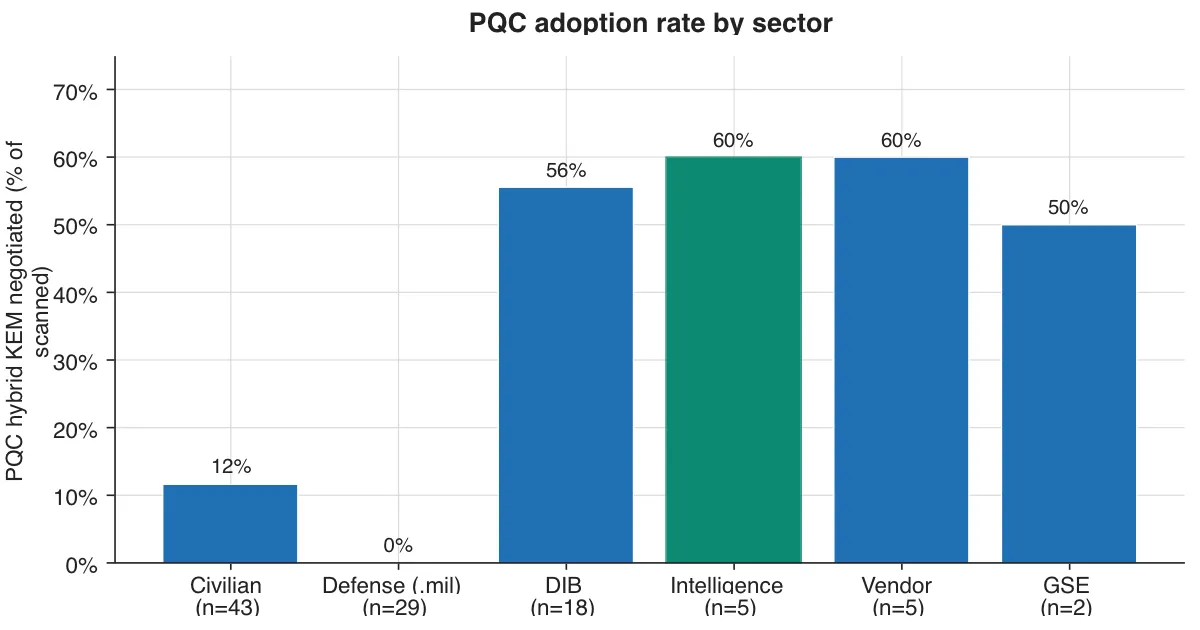
Public Sector TLS Trends, Issue 0: Methodology and Inaugural Snapshot
A new recurring series tracking what the CA/Browser Forum SC-081v3 validity reductions, the dismantling of OCSP, and post-quantum handshake adoption actually look like in the federal public web. Issue 0 establishes methodology and presents the 2026-05-03 baseline.
 Part 2·May 13, 2026
Public Sector TLS Trends, Addendum to Issue 0: Apex vs www, Two Cert Programs on One Domain
Issue 0 surfaced one civilian agency with an expired apex cert and a healthy www. This addendum extends the methodology to the full inventory: 28 of 109 entities (26 percent) run two cert programs on one domain, concentrated in civilian agencies and absent from the defense industrial base.
- Part 3·May 18, 2026
Public Sector TLS Trends, Week of 2026-05-17
Three civilian agency sites rotated this week from long-validity DigiCert leaves to fresh 198-day DigiCert leaves — the first wave of federal civilian sites in the dataset to step off the pre-SC-081v3 long-validity cohort and land cleanly under the 200-day cap.
- Part 4·May 26, 2026
Public Sector TLS Trends, Week of 2026-05-26
Twelve .mil hosts that shared a 2026-06-03 Let's Encrypt expiration all rotated on the same day to a new synchronized 2026-08-17 expiry, confirming the single-CDN-tenant batch-issuance pattern as a two-cycle trend.
- Part 5·June 9, 2026
Public Sector TLS Trends, Bi-Weekly Update for 2026-06-09
The GSE-sector postal site flagged two weeks ago renewed under the SC-081v3 validity cap at 198 days, and it did not arrive alone: leaves carrying more than 200 days of validity fell from 37 to 34 as the cap reached the next cohort.